Accelerators
Third-Party Vulnerability Assessment AI Agent
THE PROBLEM
Modern enterprises depend on hundreds of third-party vendors, SaaS platforms, and supply-chain partners, each one an extension of the attack surface. Yet most third-party risk programs still rely on annual questionnaires, static SIG/SOC 2 document reviews, and self-attested compliance checklists. These point-in-time snapshots are stale the moment they're submitted: a vendor's security posture can change overnight through a new CVE, a misconfigured cloud bucket, or a breach at one of their own sub-processors, and none of it is visible until the next review cycle, or until an incident forces it into view. Security and procurement teams are left manually cross-referencing lengthy PDFs and spreadsheets, unable to prioritize which vendors pose real, exploitable risk versus which simply have paperwork gaps. The result is a third-party risk program that looks compliant on paper while remaining structurally blind in practice.
OUR SOLUTION
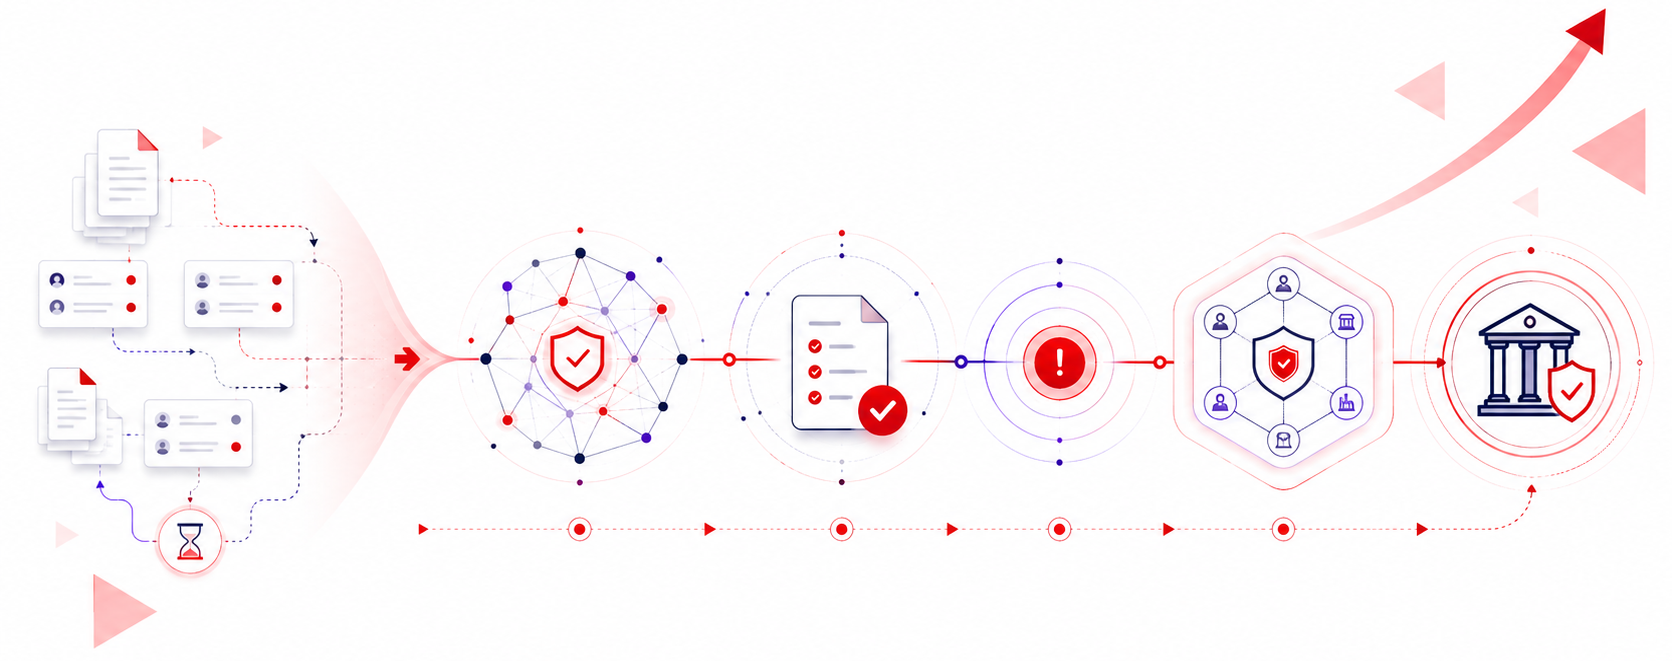
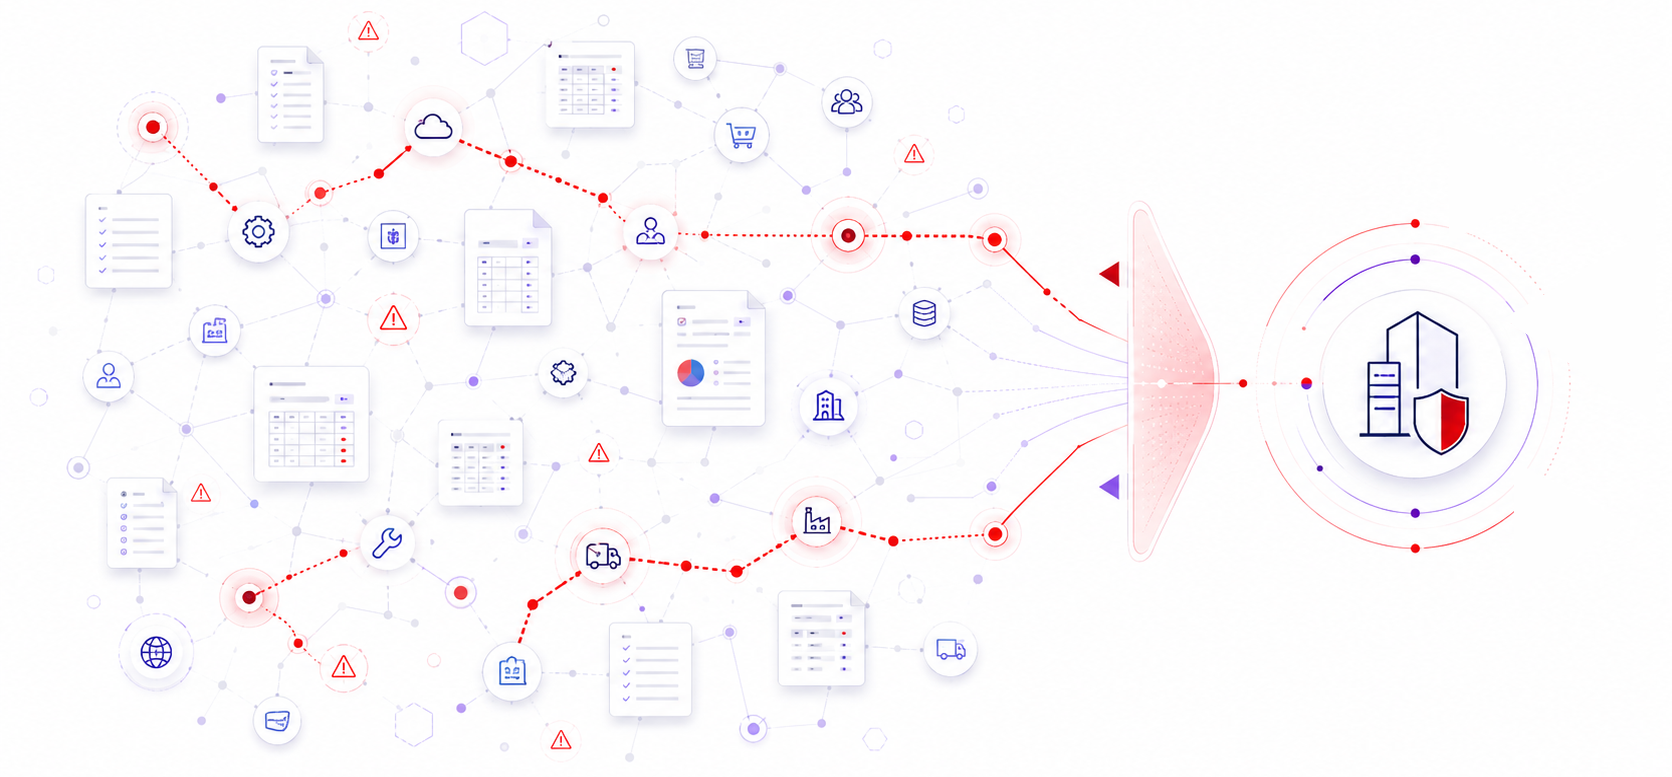
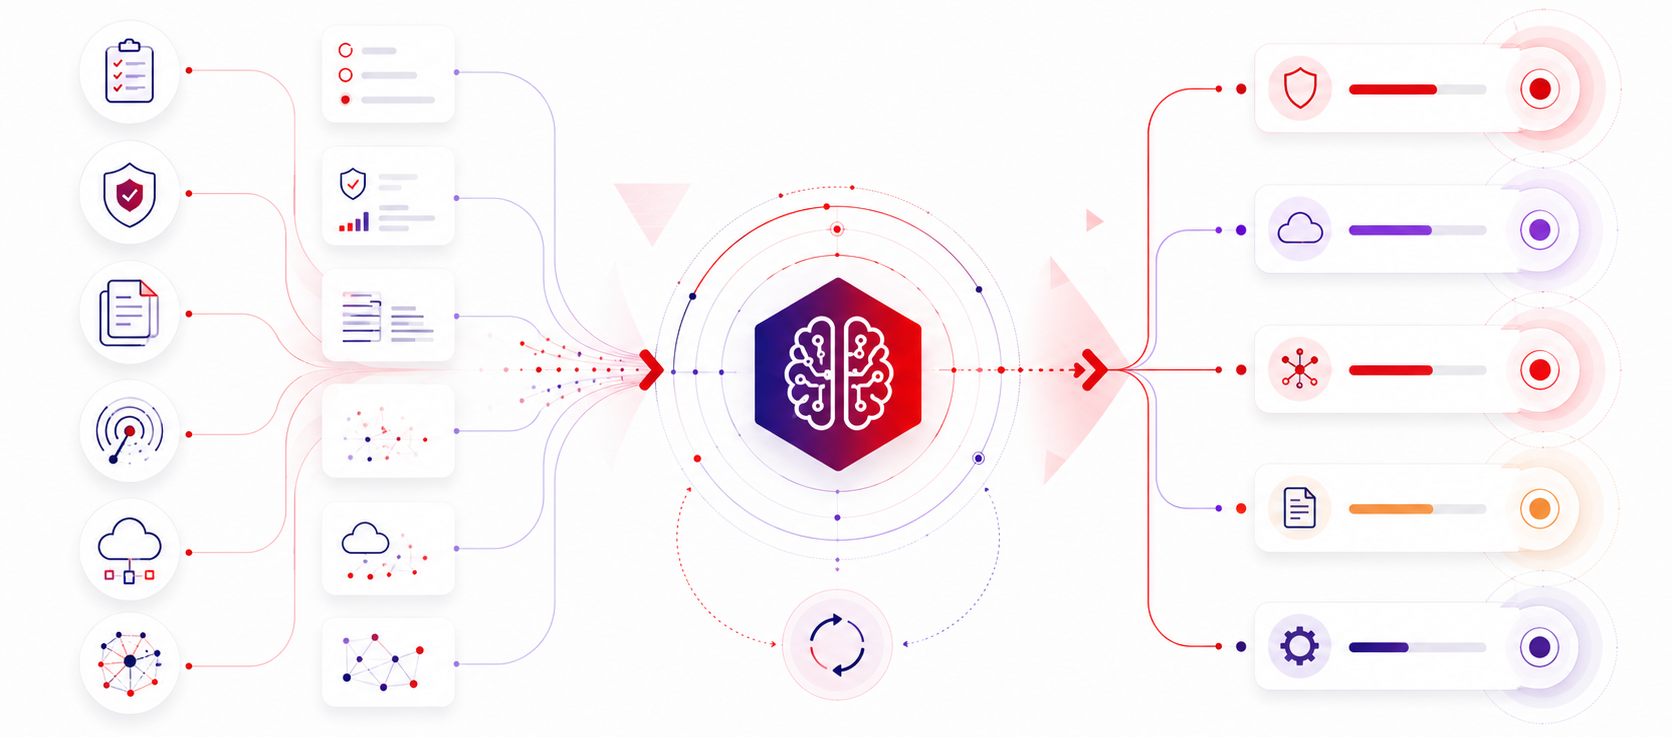
The 3P Vulnerability Assessment replaces static, once-a-year reviews with continuous, automated vendor risk intelligence. The platform ingests vendor questionnaires, SOC 2 and ISO reports, and public attack-surface data, using AI to read, extract, and validate control evidence in minutes instead of weeks. It then continuously monitors each vendor's external footprint for exposed assets, unpatched CVEs, leaked credentials, and threat intel signals, correlating findings into a single, living risk score per vendor. Instead of a checkbox questionnaire result, security teams get a real-time, evidence-backed view of which vendors are actually safe to trust today.
WHAT MAKES IT UNIQUE
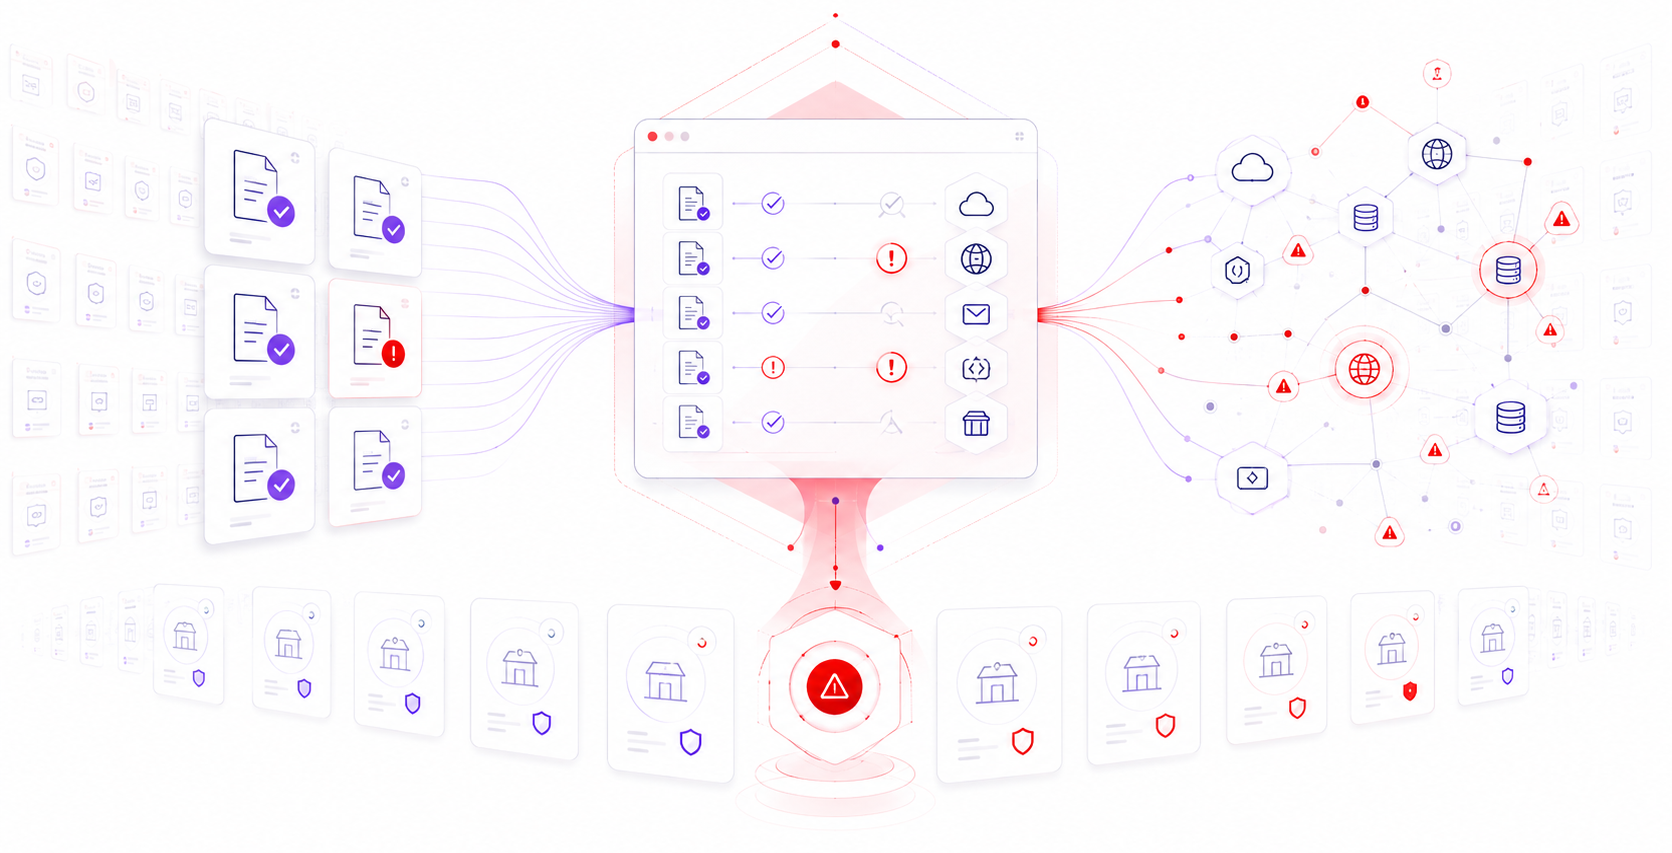
Where traditional third-party risk tools stop at document collection, this platform closes the loop between paperwork and reality: it cross-validates what a vendor claims in their questionnaire against what their live external attack surface actually shows, automatically flagging discrepancies a manual reviewer would miss. Risk scoring is continuous and evidence-driven rather than a static annual snapshot, so a new vendor vulnerability or breach disclosure updates that vendor's risk posture the moment it's detected. And because assessment is AI-automated end to end, from document parsing to exploitability correlation, the program scales across hundreds of vendors without scaling headcount.
INNOVATIVE APPROACHES, METHODS & TECHNOLOGIES
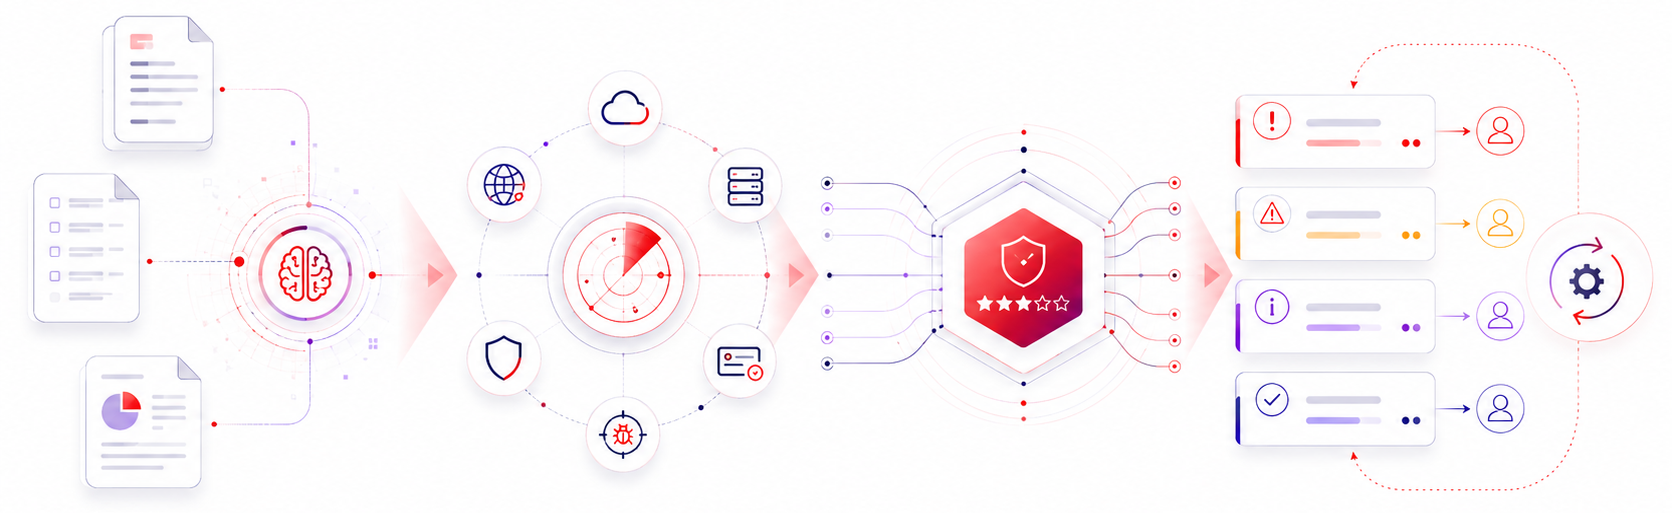
An LLM-powered document intelligence engine automatically parses vendor questionnaires, SIG/SOC 2/ISO reports, and contracts, extracting control claims and flagging inconsistencies or missing evidence without manual review.
Continuous external attack surface monitoring scans each vendor's public-facing infrastructure for exposed services, known CVEs, expired certificates, and leaked credentials, keeping risk data current between assessment cycles.
A correlation and scoring engine fuses self-reported control evidence with live threat intelligence and exploitability data, producing a single, defensible risk score per vendor rather than a raw findings list.
Automated workflows route high-risk findings to owners with plain-language remediation guidance and re-assessment triggers, turning vendor risk management from a periodic audit into a continuous operating process.
THE IMPACT WE AIM TO ACHIEVE
By shifting third-party risk management from static, point-in-time reviews to continuous, evidence-based monitoring, we aim to cut vendor assessment turnaround from weeks to hours, surface real exploitable risk that questionnaires alone miss, and give security and procurement teams a defensible, always-current view of vendor posture. The result is a third-party risk program that reflects reality, not just paperwork, closing supply-chain blind spots before they become breaches.